Cybersecurity Alert: New Federal Warnings on Data Breaches Affecting 15% of U.S. Businesses in Q1 2026. (RECENT UPDATES)
In an increasingly digital world, the threat of cyberattacks looms larger than ever. Recent federal data breach warnings have sent ripples through the U.S. business community, highlighting a critical need for enhanced cybersecurity measures. As we navigate the complex landscape of digital threats, understanding the scope and implications of these warnings is paramount for every organization.
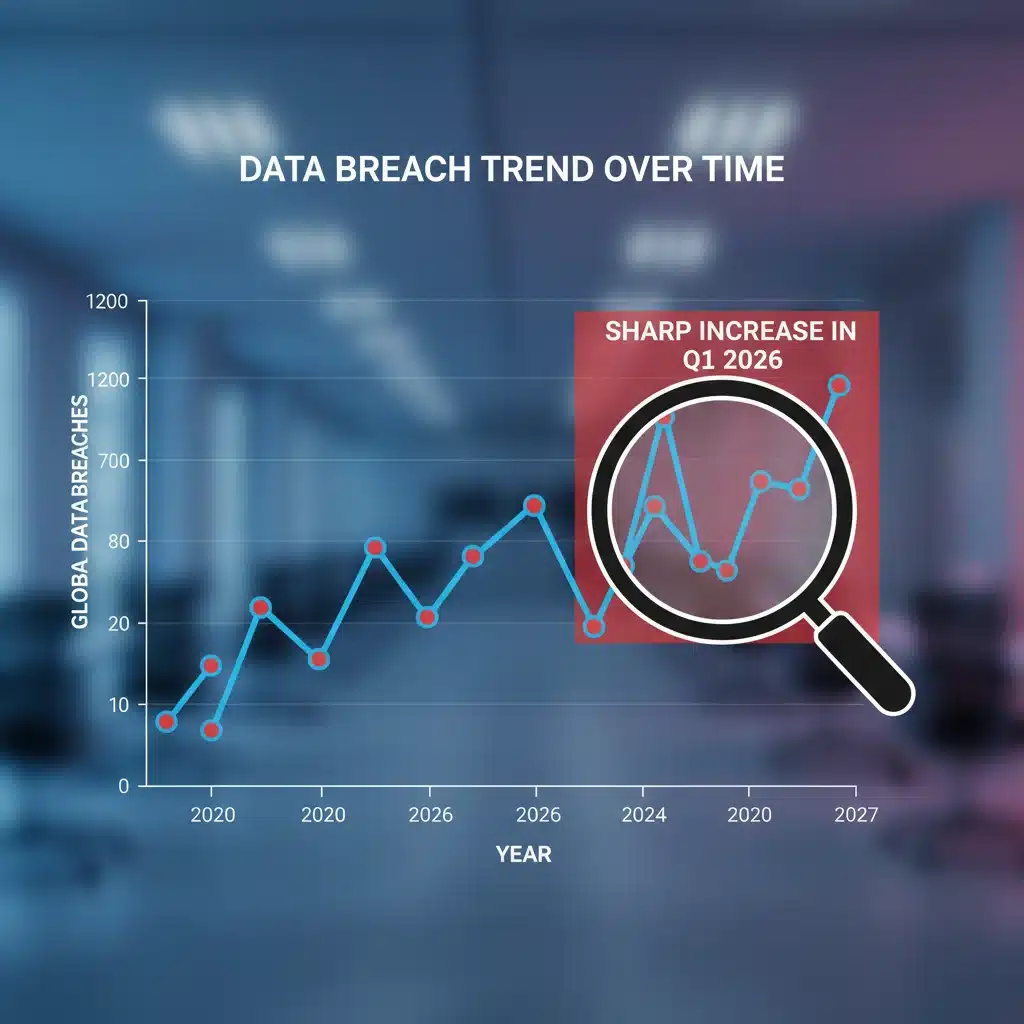
The first quarter of 2026 has brought with it sobering statistics: an estimated 15% of U.S. businesses have already been impacted by data breaches. This figure, released by federal cybersecurity agencies, underscores a disturbing trend of escalating cyber threats. These federal data breach warnings are not mere advisories; they are urgent calls to action, demanding immediate attention and robust responses from businesses of all sizes. The financial, reputational, and operational consequences of a data breach can be catastrophic, making proactive defense an absolute necessity.
This comprehensive guide delves into the specifics of these federal data breach warnings, explores the common vectors of attack, and provides actionable strategies for businesses to protect themselves. We will also examine the regulatory landscape, emphasizing compliance and accountability in the face of these evolving threats. Our aim is to equip you with the knowledge and tools necessary to fortify your digital defenses and safeguard your valuable assets against the relentless tide of cybercrime.
The Escalating Threat Landscape: Understanding Federal Data Breach Warnings
The digital frontier is constantly expanding, and with it, the opportunities for malicious actors to exploit vulnerabilities. The latest federal data breach warnings paint a stark picture of a threat landscape that is more sophisticated and pervasive than ever before. Cybercriminals are employing advanced techniques, from highly targeted phishing campaigns to complex ransomware attacks, to gain unauthorized access to sensitive data.
One of the primary concerns highlighted in these federal data breach warnings is the increasing success rate of these attacks. The statistic that 15% of U.S. businesses have been affected in Q1 2026 is not just a number; it represents countless hours of lost productivity, significant financial drains, and often, irreparable damage to customer trust. Small and medium-sized businesses (SMBs), often perceived as less secure targets, are particularly vulnerable, lacking the extensive resources of larger corporations to invest in cutting-edge cybersecurity infrastructure.
The types of data compromised in these breaches are varied, including personally identifiable information (PII), financial records, intellectual property, and trade secrets. The exposure of such data can lead to identity theft, fraud, competitive disadvantages, and severe regulatory penalties. The federal data breach warnings emphasize that no industry is immune, and businesses across all sectors must prioritize their cybersecurity posture.
Key Factors Contributing to the Surge in Breaches
- Remote Work Vulnerabilities: The widespread adoption of remote and hybrid work models has expanded the attack surface, creating new entry points for cybercriminals. Home networks often lack the robust security measures found in corporate environments, making them easier targets.
- Sophisticated Phishing and Social Engineering: Attackers are becoming more adept at crafting convincing phishing emails and social engineering tactics, tricking employees into revealing credentials or downloading malware.
- Supply Chain Attacks: Compromising a single vendor can provide access to multiple organizations further down the supply chain. These attacks are particularly insidious as they leverage trusted relationships.
- Ransomware as a Service (RaaS): The proliferation of RaaS models has lowered the barrier to entry for aspiring cybercriminals, making ransomware attacks more frequent and widespread.
- Unpatched Software and Systems: Many organizations fail to keep their software and systems updated, leaving known vulnerabilities open for exploitation.
These factors, combined with a persistent shortage of cybersecurity professionals, create a challenging environment for businesses striving to protect their digital assets. The federal data breach warnings serve as a critical reminder that vigilance and continuous adaptation are essential in this ongoing battle.
The Economic and Reputational Toll of Data Breaches
Beyond the immediate disruption, the long-term consequences of a data breach can be devastating for businesses. The economic toll is multifaceted, encompassing direct costs such as incident response, forensic investigations, legal fees, and regulatory fines, as well as indirect costs like lost business, reputational damage, and increased insurance premiums. The federal data breach warnings highlight that these costs are escalating, making prevention more cost-effective than remediation.
According to various industry reports, the average cost of a data breach continues to rise year over year. For SMBs, a single breach can be financially ruinous, with many forced to close their doors within months of an incident. Larger enterprises, while often more resilient, still face significant financial setbacks and the potential for class-action lawsuits.
Reputational damage is another critical consequence. Customers entrust businesses with their personal and financial information, and a breach of that trust can be difficult, if not impossible, to repair. News of a data breach spreads rapidly, eroding customer confidence and leading to churn. This negative publicity can also deter prospective clients and make it challenging to attract and retain talent. The federal data breach warnings emphasize the importance of transparent communication and swift action in the aftermath of a breach to mitigate reputational harm.
Regulatory Implications and Compliance
The regulatory landscape surrounding data privacy and security is becoming increasingly stringent. Federal data breach warnings are often accompanied by reminders of existing regulations and the potential for new ones. Laws such as the California Consumer Privacy Act (CCPA), the General Data Protection Regulation (GDPR) (for businesses with European customers), and industry-specific regulations like HIPAA for healthcare or PCI DSS for payment card data, impose strict requirements on how organizations handle and protect sensitive information.
Non-compliance can result in substantial fines and legal penalties, further exacerbating the financial burden of a data breach. The federal data breach warnings encourage businesses to conduct regular audits and assessments to ensure they are meeting all relevant regulatory obligations. Developing a robust compliance framework is not just about avoiding penalties; it’s about demonstrating a commitment to data protection, which can enhance customer trust and brand loyalty.
Proactive Strategies: Fortifying Your Defenses Against Federal Data Breach Warnings
Responding to federal data breach warnings effectively requires a multi-layered, proactive approach to cybersecurity. Businesses must move beyond reactive measures and implement comprehensive strategies that address both technological and human elements of security. Here are key areas of focus:
1. Robust Employee Training and Awareness
The human element remains the weakest link in many security chains. Regular, engaging, and up-to-date cybersecurity training is crucial. Employees should be educated on identifying phishing attempts, recognizing social engineering tactics, practicing strong password hygiene, and understanding the importance of reporting suspicious activities. These federal data breach warnings highlight that a well-informed workforce is your first line of defense.
2. Implementing Strong Access Controls
Limiting access to sensitive data on a ‘need-to-know’ basis is fundamental. Implement multi-factor authentication (MFA) for all accounts, especially those with privileged access. Regularly review and update access permissions to ensure they align with current roles and responsibilities. The federal data breach warnings emphasize that compromised credentials are a leading cause of breaches.
3. Regular Software Updates and Patch Management
Vulnerabilities in software and operating systems are frequently exploited by attackers. Establish a rigorous patch management program to ensure all systems are updated promptly. Automate updates whenever possible to minimize human error and ensure timely application of security patches. This is a recurring theme in federal data breach warnings.
4. Data Encryption
Encrypting sensitive data, both in transit and at rest, adds an essential layer of protection. Even if attackers gain access to your systems, encrypted data will be significantly harder to decipher, reducing the impact of a breach. This is a critical recommendation from federal data breach warnings for protecting sensitive information.
5. Comprehensive Backup and Recovery Plan
In the event of a ransomware attack or data corruption, a robust backup and recovery plan is invaluable. Regularly back up all critical data to secure, offsite locations and test your recovery procedures periodically to ensure their effectiveness. The federal data breach warnings stress that reliable backups can be the difference between recovery and ruin.
6. Network Segmentation
Segmenting your network can limit the lateral movement of attackers within your infrastructure. By isolating critical systems and data, you can contain the damage of a breach and prevent it from spreading throughout your entire network. This strategy is often recommended in federal data breach warnings for larger organizations.
7. Endpoint Detection and Response (EDR)
Deploy EDR solutions to monitor endpoints for suspicious activity, detect threats in real-time, and automate responses. EDR tools provide greater visibility into your network and can help identify and neutralize threats before they cause significant damage. These tools are increasingly vital given the sophistication of modern attacks, as noted in federal data breach warnings.
8. Incident Response Plan (IRP)
Even with the best defenses, a breach can still occur. A well-defined and regularly tested Incident Response Plan is crucial for minimizing the impact. This plan should outline clear steps for identifying, containing, eradicating, recovering from, and learning from a security incident. The federal data breach warnings underscore the necessity of a prepared response.
9. Vendor Risk Management
As supply chain attacks become more prevalent, it’s essential to assess the cybersecurity posture of your third-party vendors and partners. Ensure that your contracts include robust security clauses and conduct regular due diligence on their security practices. This is a growing area of concern highlighted in federal data breach warnings.
10. Regular Security Audits and Penetration Testing
Periodically engage external experts to conduct security audits and penetration testing. These assessments can identify vulnerabilities that internal teams might overlook and provide valuable insights into your security posture. Acting on the findings from these tests is critical for continuous improvement, as advised by federal data breach warnings.
The Role of Federal Agencies in Cybersecurity
Federal agencies play a pivotal role in issuing federal data breach warnings and guiding businesses through the complex world of cybersecurity. Organizations like the Cybersecurity and Infrastructure Security Agency (CISA), the National Institute of Standards and Technology (NIST), and the FBI’s Internet Crime Complaint Center (IC3) provide invaluable resources, threat intelligence, and best practices.
CISA, in particular, is at the forefront of identifying and mitigating cyber threats. Their alerts and advisories, which form the basis of many federal data breach warnings, are designed to inform critical infrastructure and businesses about emerging vulnerabilities and attack campaigns. NIST provides comprehensive frameworks, such as the NIST Cybersecurity Framework, which offers a flexible and actionable approach to managing cybersecurity risk.
Businesses are strongly encouraged to subscribe to alerts from these agencies, participate in information-sharing initiatives, and leverage the wealth of resources they provide. Collaboration between the private sector and government is essential to build a resilient national cybersecurity posture, a key message embedded within the federal data breach warnings.
Upcoming Regulations and Future Outlook
The landscape of cybersecurity regulations is continually evolving. In response to the increasing frequency and severity of data breaches, it is highly probable that new federal data privacy and security laws will be enacted or existing ones strengthened. These potential regulations could introduce more stringent reporting requirements, higher penalties for non-compliance, and expanded rights for consumers regarding their data.
Businesses should anticipate these changes and begin preparing now. Staying abreast of legislative developments, engaging with industry associations, and adapting security strategies to meet future compliance demands will be crucial. The federal data breach warnings serve as a precursor to a more regulated future, where accountability for data protection will be even more pronounced.
Looking ahead, the trend of increasing cyber threats is expected to continue. The advent of artificial intelligence (AI) and quantum computing presents both opportunities and challenges for cybersecurity. While AI can enhance defensive capabilities, it can also be leveraged by attackers to create more sophisticated and potent threats. Businesses must continuously innovate and adapt their security strategies to keep pace with these technological advancements. The federal data breach warnings are not a one-time event but a continuous reminder of an ongoing challenge.
Conclusion: A Call to Action for Every U.S. Business
The recent federal data breach warnings, indicating that 15% of U.S. businesses have been affected in Q1 2026, serve as an unequivocal wake-up call. The era of assuming ‘it won’t happen to us’ is over. Cybersecurity is no longer just an IT issue; it is a fundamental business imperative that requires attention from the boardroom to every employee.
Protecting your organization from data breaches demands a proactive, multi-faceted strategy that combines robust technological solutions with comprehensive employee training and a strong culture of security. By implementing the strategies outlined in this guide, businesses can significantly reduce their risk exposure and build a more resilient defense against the ever-present threat of cyberattacks.
Heed the federal data breach warnings. Invest in your cybersecurity infrastructure, educate your workforce, and develop a comprehensive incident response plan. The cost of prevention pales in comparison to the potential devastation of a successful data breach. Secure your future by securing your data today.