2026 Cybersecurity Legislation: U.S. Business Compliance Guide & Updates
Navigating the New 2026 Cybersecurity Legislation: A U.S. Business Imperative
The digital landscape is constantly evolving, and with it, the threats posed to businesses of all sizes. In response to these escalating risks, the United States government is rolling out comprehensive New 2026 Cybersecurity Legislation designed to bolster national security and protect sensitive data. For U.S. businesses, this isn’t just another regulatory hurdle; it’s a fundamental shift in how cybersecurity is approached and managed. Failing to understand and comply with these new mandates could lead to significant financial penalties, reputational damage, and operational disruptions. This extensive guide aims to demystify the upcoming changes, provide actionable insights, and equip your business with the knowledge needed to ensure full compliance and thrive in a more secure digital future.
The concept of cybersecurity legislation 2026 is not merely about adding new rules; it’s about establishing a robust framework that reflects the current threat landscape and anticipates future challenges. Businesses that proactively embrace these changes will not only avoid penalties but also gain a competitive edge by demonstrating a strong commitment to data protection and trust. This article will delve into the core components of the new legislation, highlight key areas of impact, and offer a strategic roadmap for compliance.
Understanding the Genesis of the New 2026 Cybersecurity Legislation
The journey towards the New 2026 Cybersecurity Legislation has been a long one, driven by a confluence of factors. The increasing frequency and sophistication of cyberattacks, the growing economic impact of data breaches, and the geopolitical implications of cyber warfare have all contributed to the urgent need for a unified and comprehensive regulatory response. Previous legislative efforts, while important, often operated in silos or lacked the necessary teeth to enforce widespread change. The cybersecurity legislation 2026 aims to address these shortcomings by creating a more integrated, proactive, and enforceable set of standards.
Key Drivers Behind the Legislation:
- Escalating Cyber Threats: Ransomware, supply chain attacks, and state-sponsored cyber espionage have become commonplace, impacting critical infrastructure, government agencies, and private enterprises.
- Economic Impact: The financial costs associated with data breaches, including recovery, legal fees, and reputational damage, are astronomical and continue to rise.
- Data Privacy Concerns: Public demand for stronger data privacy protections has pressured lawmakers to enact stricter rules governing how personal information is collected, stored, and processed.
- Global Harmonization: While not fully harmonized, there’s a growing international push for common cybersecurity standards, and the U.S. legislation seeks to align with global best practices where appropriate.
These drivers underscore the criticality of the New 2026 Cybersecurity Legislation. It’s a response to a clear and present danger, and businesses must treat it with the seriousness it deserves.
Core Components of the Cybersecurity Legislation 2026
While the final details are still being refined, several core components are expected to form the bedrock of the cybersecurity legislation 2026. These components will likely touch upon various aspects of an organization’s cybersecurity posture, from incident reporting to supply chain risk management.
Mandatory Incident Reporting:
One of the most significant changes will be the introduction of mandatory and timely incident reporting requirements. Businesses will likely be required to report significant cyber incidents to a designated federal agency within a very short timeframe (e.g., 24-72 hours). This aims to:
- Improve national situational awareness of cyber threats.
- Facilitate faster response and coordination among government agencies and affected entities.
- Enable better threat intelligence sharing to prevent future attacks.
Businesses will need robust incident response plans and capabilities to meet these strict reporting deadlines. This includes clear internal communication protocols, forensic analysis capabilities, and established channels for reporting to external authorities.
Enhanced Data Protection Standards:
The legislation will likely mandate stricter data protection standards, focusing on encryption, access controls, and data minimization. This will extend beyond personally identifiable information (PII) to include other sensitive business data, intellectual property, and critical operational technology (OT) data. Companies will need to:
- Implement advanced encryption for data at rest and in transit.
- Strengthen multi-factor authentication (MFA) and granular access controls.
- Conduct regular data inventories and ensure data retention policies align with legal requirements.
Supply Chain Cybersecurity Requirements:
Recognizing that many cyberattacks originate through third-party vendors, the cybersecurity legislation 2026 will place a greater emphasis on supply chain cybersecurity. Businesses will be expected to conduct due diligence on their vendors, assess their cybersecurity postures, and potentially mandate specific security controls in contracts. This means:
- Developing a comprehensive vendor risk management program.
- Incorporating cybersecurity clauses into all vendor agreements.
- Regularly auditing third-party security practices.
Risk Management Frameworks:
The legislation is expected to encourage or mandate the adoption of recognized cybersecurity risk management frameworks, such as the NIST Cybersecurity Framework. These frameworks provide a structured approach to identifying, assessing, managing, and responding to cyber risks. Implementing such a framework involves:
- Conducting regular risk assessments to identify vulnerabilities and threats.
- Developing and implementing security policies and procedures.
- Continuously monitoring and improving cybersecurity controls.
Accountability and Governance:
Increased accountability for cybersecurity at the executive and board level is also anticipated. This could involve requirements for board-level cybersecurity expertise, regular reporting to leadership, and clear delineation of cybersecurity responsibilities within the organization. This shift aims to elevate cybersecurity from a purely IT concern to a strategic business imperative.
Who Will Be Affected by the Cybersecurity Legislation 2026?
While specific industry sectors might have tailored requirements, the overarching goal of the New 2026 Cybersecurity Legislation is to create a baseline level of security across a broad spectrum of U.S. businesses. It’s safe to assume that any entity handling sensitive data, operating critical infrastructure, or engaging in interstate commerce will be impacted.
Likely Affected Sectors:
- Critical Infrastructure: Energy, water, transportation, healthcare, communications, and financial services will undoubtedly face stringent requirements due to their systemic importance.
- Technology Companies: Software developers, cloud service providers, and hardware manufacturers will be scrutinized for their role in the digital supply chain.
- Small and Medium-sized Businesses (SMBs): While perhaps with scaled requirements, SMBs will not be exempt, especially if they handle significant customer data or are part of larger supply chains.
- Any Business Handling Sensitive Data: This includes PII, protected health information (PHI), financial data, and intellectual property.
The breadth of impact means that no U.S. business can afford to ignore the upcoming changes. Proactive assessment of current cybersecurity practices against anticipated legislative requirements is paramount.
Preparing Your Business for Compliance: A Strategic Roadmap
Achieving compliance with the cybersecurity legislation 2026 will require a strategic and sustained effort. It’s not a one-time project but an ongoing commitment to cybersecurity excellence. Here’s a roadmap to guide your preparation:
1. Conduct a Comprehensive Cybersecurity Assessment:
Before you can improve, you need to know where you stand. A thorough assessment will identify your current vulnerabilities, compliance gaps, and areas needing immediate attention. This should include:
- Gap Analysis: Compare your existing security controls against proposed legislative requirements and recognized frameworks like NIST.
- Vulnerability Assessments & Penetration Testing: Actively test your systems for weaknesses.
- Data Mapping: Understand what sensitive data you collect, where it’s stored, who has access, and how it flows through your systems.
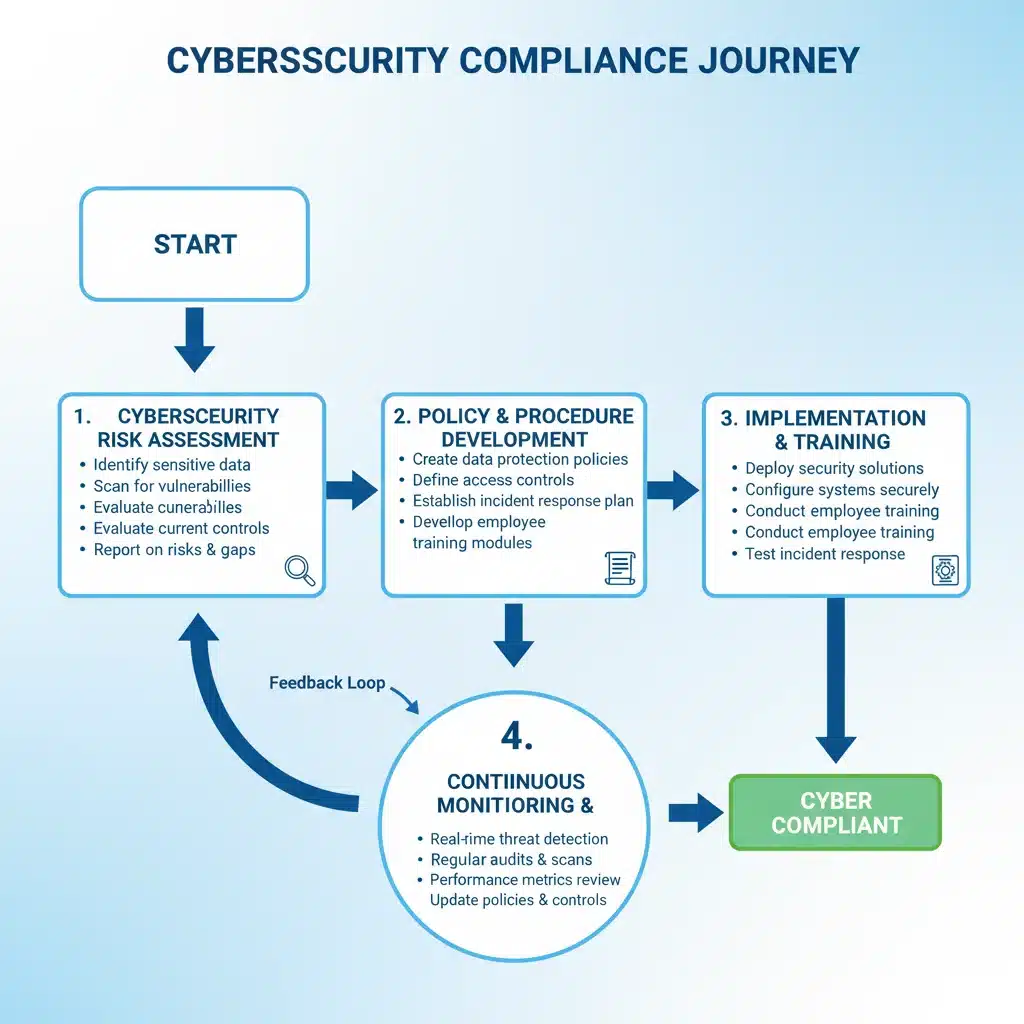
2. Develop and Update Cybersecurity Policies and Procedures:
Formal policies are the backbone of any strong cybersecurity program. You’ll need to review and update existing policies, and create new ones, to align with the cybersecurity legislation 2026. Key areas include:
- Incident Response Plan: Detailed steps for detection, containment, eradication, recovery, and post-incident analysis.
- Data Protection Policy: Guidelines for data classification, encryption, access control, and retention.
- Vendor Risk Management Policy: Procedures for assessing and managing third-party security risks.
- Employee Training Policy: Mandating regular cybersecurity awareness training for all staff.
3. Implement Robust Technical Controls:
Policies are only effective if backed by strong technical controls. Invest in and implement technologies that enhance your security posture:
- Advanced Endpoint Protection: Next-generation antivirus, endpoint detection and response (EDR).
- Network Segmentation: Isolate critical systems to limit the impact of a breach.
- Security Information and Event Management (SIEM): Centralize log collection and analysis for threat detection.
- Data Loss Prevention (DLP): Prevent sensitive data from leaving your organization’s control.
- Identity and Access Management (IAM): Strong authentication and authorization controls.
4. Prioritize Employee Training and Awareness:
Your employees are often the first line of defense, but also the most common point of failure. Regular, engaging cybersecurity awareness training is non-negotiable. This should cover:
- Phishing and social engineering recognition.
- Strong password practices and MFA usage.
- Safe browsing habits and secure data handling.
- Incident reporting procedures.
5. Strengthen Third-Party Risk Management:
As mentioned, supply chain security is a major focus. Proactively engage with your vendors:
- Review existing contracts and add cybersecurity clauses.
- Require vendors to demonstrate their security posture through certifications or assessments.
- Establish clear communication channels for security incidents involving third parties.
6. Allocate Adequate Resources:
Compliance with the cybersecurity legislation 2026 will require financial investment and dedicated personnel. This might mean hiring additional cybersecurity staff, engaging external consultants, or investing in new security technologies. View these as investments in your business’s resilience and long-term viability.
7. Establish a Culture of Cybersecurity:
Ultimately, compliance is about more than just checking boxes; it’s about embedding cybersecurity into your organizational culture. This means:
- Leadership buy-in and active participation.
- Continuous improvement and adaptation to new threats.
- Encouraging a security-first mindset among all employees.
Potential Penalties for Non-Compliance
The New 2026 Cybersecurity Legislation is expected to carry significant penalties for non-compliance. These penalties are designed to be a strong deterrent and ensure that businesses take their cybersecurity responsibilities seriously. The exact nature and scale of penalties will vary depending on the severity of the violation, the size of the business, and the impact of any resulting breach.
Types of Penalties May Include:
- Financial Fines: These could be substantial, potentially calculated per incident, per record compromised, or as a percentage of annual revenue, similar to GDPR.
- Legal Action and Litigation: Non-compliant businesses may face lawsuits from affected individuals, customers, or even government agencies.
- Reputational Damage: Public disclosure of non-compliance or a breach can severely damage a business’s reputation, leading to loss of customer trust and market share.
- Operational Disruptions: Regulatory investigations, mandates for system overhauls, or even temporary cessation of operations can severely impact business continuity.
- Loss of Business Opportunities: Non-compliance could lead to exclusion from government contracts or partnerships with other businesses that demand strict adherence to cybersecurity standards.
The potential for these severe consequences underscores why proactive compliance with the cybersecurity legislation 2026 is not optional but essential for business survival and growth in the coming years.
The Long-Term Impact on U.S. Businesses
Beyond avoiding penalties, adhering to the New 2026 Cybersecurity Legislation offers several long-term benefits for U.S. businesses. This legislation is not just about regulation; it’s about fostering a more secure and resilient digital economy.
Increased Trust and Confidence:
Businesses that demonstrate strong cybersecurity practices will earn greater trust from customers, partners, and investors. In an era where data breaches are common, a commitment to security can be a significant differentiator.
Enhanced Competitive Advantage:
Compliance can become a competitive advantage, especially when dealing with businesses that prioritize security in their supply chains. Being able to certify adherence to robust standards can open doors to new opportunities.
Improved Operational Resilience:
By implementing the required controls, businesses will inherently improve their overall operational resilience. They will be better equipped to withstand cyberattacks, recover quickly from incidents, and maintain business continuity.
Better Threat Intelligence and Collaboration:
Mandatory reporting and increased information sharing fostered by the legislation will lead to a more comprehensive understanding of the threat landscape, benefiting all businesses within the ecosystem.
Innovation in Cybersecurity:
The demand for compliance will spur innovation in cybersecurity products, services, and solutions, creating a more dynamic and effective market for security tools.
Staying Informed: Continuous Monitoring and Adaptation
The digital threat landscape is dynamic, and so too will be the interpretation and enforcement of the cybersecurity legislation 2026. Businesses must commit to continuous monitoring and adaptation to remain compliant.
Key Strategies for Staying Informed:
- Subscribe to Official Updates: Follow government agencies (e.g., CISA, NIST) for official announcements and guidance.
- Engage with Industry Associations: Many industry-specific associations will provide tailored guidance and resources.
- Consult Legal and Cybersecurity Experts: Leverage external expertise to interpret complex regulations and ensure your compliance strategy is sound.
- Regularly Review and Update Policies: Cybersecurity policies and procedures should not be static; they need to evolve with the threats and regulatory landscape.
The proactive approach to cybersecurity is no longer a luxury but a necessity. The New 2026 Cybersecurity Legislation represents a significant step towards a more secure digital future for U.S. businesses. By understanding its implications, developing a robust compliance strategy, and fostering a culture of security, businesses can navigate these changes successfully, protect their assets, and maintain trust in an increasingly interconnected world.
Conclusion: A Call to Action for U.S. Businesses
The New 2026 Cybersecurity Legislation marks a pivotal moment for U.S. businesses. It underscores the critical importance of cybersecurity as a fundamental aspect of business operations, not merely an IT concern. The days of reactive security measures are over; the future demands proactive, comprehensive, and continuously evolving cybersecurity strategies. Businesses that embrace the requirements of the cybersecurity legislation 2026 will not only safeguard themselves against severe penalties but also build stronger, more resilient, and more trusted enterprises.
Start your preparation today. Conduct thorough assessments, invest in appropriate technologies, train your workforce, and foster a culture where cybersecurity is everyone’s responsibility. The digital future is secure for those who are prepared.